The Microsoft outage took email from Norway's parliament and ministries. Europe and Norway must act now.
For around 20 hours on 12 and 13 November 2026, Microsoft's email service failed for users in at least 74 countries, and in Norway it reached the Storting, the Norwegian parliament, and most ministries. One company, under the law of one country, carries the daily communication of a large share of Europe's businesses and public bodies. This week showed what that costs, and what Europe and Norway can change.
What failed, and when
Exchange Online, the service behind Outlook, began to fail late in the afternoon of Thursday 12 November, European time. Microsoft posted its first notice at 17:54 UTC under incident EX1550543, about mailbox access in the Americas, and within the hour said users in any region could be affected. A wider incident, MO1550821, covered services that depend on Exchange, among them Teams, SharePoint Online, Microsoft 365 Copilot and Defender XDR, according to BleepingComputer and SecurityWeek.
Downdetector logged close to 140,000 Outlook reports at the peak on Thursday evening, from 74 countries and territories, according to Euronews and NRK. Downdetector counts only the people who file a report.
Microsoft first described elevated load, then “a number of servers being unexpectedly unavailable; straining the remaining infrastructure”. Early on 13 November it said a process that establishes secure connections on the affected servers was overwhelmed, and that it had “begun reverting a recent network configuration change that correlates with the start of impact”. Servers brought back overnight dropped out again when traffic returned, ABC News reported. Microsoft says it has no evidence of malicious activity and has promised a post-incident report with the root cause.
Around 14:00 UTC on Friday, Microsoft said mail queues were approaching normal levels, and it had extended the time it holds delayed mail to 48 hours (CNBC, BleepingComputer). When we published, Microsoft had not declared the incident resolved.
Parliament, the ministries, the hospitals
All 169 members of the Storting and its administration lost access to email, the administration told TV 2, as Nettavisen reported. The problems reached every ministry except the Ministry of Justice and Public Security, the Ministry of Defence and the Office of the Prime Minister, according to DIO, the ministries' shared IT service, in a report from NTB on Digi.no. The Norwegian Digitalisation Agency stopped taking email and asked people with Altinn questions to phone, NRK reported.
Oslo University Hospital and Østfold Hospital lost administrative tools while patient treatment ran as normal, and the police reported unstable Teams meetings and calls, according to NRK and Digi.no. Voss and Kvinnherad asked residents to phone in urgent matters, and the Governor of Svalbard could not receive email, Nettavisen reported. DNB told E24 that internal email was hard to use and that its customer centre was unaffected.
Bergen municipality wrote on 13 November that email to and from the municipality was not working normally, including email notices about digital letters from the municipality, and that Teams was unstable. It warned that fraud attempts become more likely during the disruption. Helse Bergen confirmed to Bergensavisen that the health trust was affected, and the paper wrote that thousands of employees at large workplaces in Bergen felt the outage.
In Scotland, Police Scotland could not receive email, and 13 of the country's 32 councils reported disruption, according to FutureScot. In Australia, the federal police, the intelligence service ASIO and several courts were hit, ABC News reported.
Microsoft Norway's communications director, Cornelia Bjørke Hill, told NRK that nothing indicated malicious activity or a cyber attack. That matters. This outage had no attacker, and it still stopped the email of a national parliament for most of a working day.
One provider, one jurisdiction
The Norwegian government wrote on 22 April 2026 that 75 percent of entities in the Norwegian public sector use Microsoft solutions. Karianne Tung, Minister of Digitalisation and Public Governance, said: “It is safe and efficient, but it also makes us vulnerable.”
The National Security Authority (NSM) gave the same warning in Risiko 2026, published in February. The market is dominated by American companies such as Amazon, Google and Microsoft, NSM wrote, and geopolitical conflict could in the worst case make services from foreign providers hard or impossible to use. NSM director Arne Christian Haugstøyl told Altinget that services can fail without any attack, and that an organisation without reserve solutions exposes itself to far too high a risk.
It is not the first large cloud failure in recent years. AWS lost its Northern Virginia region on 19 and 20 October 2025. Azure Front Door failed on 29 October 2025 after a configuration change. Microsoft 365 was down for almost ten hours in North America on 22 and 23 January 2026. Each time, a fault in one company's systems reached customers far from where it started.
Law is the second half of the dependence. The US CLOUD Act of 2018 lets American authorities demand data from American providers wherever that data is stored. On 10 June 2025, a commission of inquiry in the French Senate asked Anton Carniaux, director of public and legal affairs at Microsoft France, whether he could guarantee under oath that French citizens' data entrusted to Microsoft through the public purchasing agency UGAP would never be handed over on an order from the US government without the explicit consent of the French authorities. He answered “No, I cannot guarantee it”, and added that it had never happened (Senate record, The Register).
What Europe has to finish
The European Commission proposed the Cloud and AI Development Act on 3 June 2026. It would give the EU a single assessment framework for cloud and AI sovereignty and a mechanism for the public sector to adopt services that meet it. Parliament and Council should adopt it with a framework that asks who operates the service and which law applies to it, and with a tested plan for moving out as a condition for cloud services sold to public bodies, so that a public body can actually change supplier.
Europe already has part of the toolkit. Since 17 January 2025, DORA (Regulation (EU) 2022/2554) has required banks, insurers and other financial entities to have exit strategies for ICT services that support critical or important functions (Article 28(8)). NIS2 (Directive (EU) 2022/2555) sets risk management duties for essential and important entities across the EU, central government included. Email and messaging belong in that scope as critical functions, with the same exit duty extended to public administration.
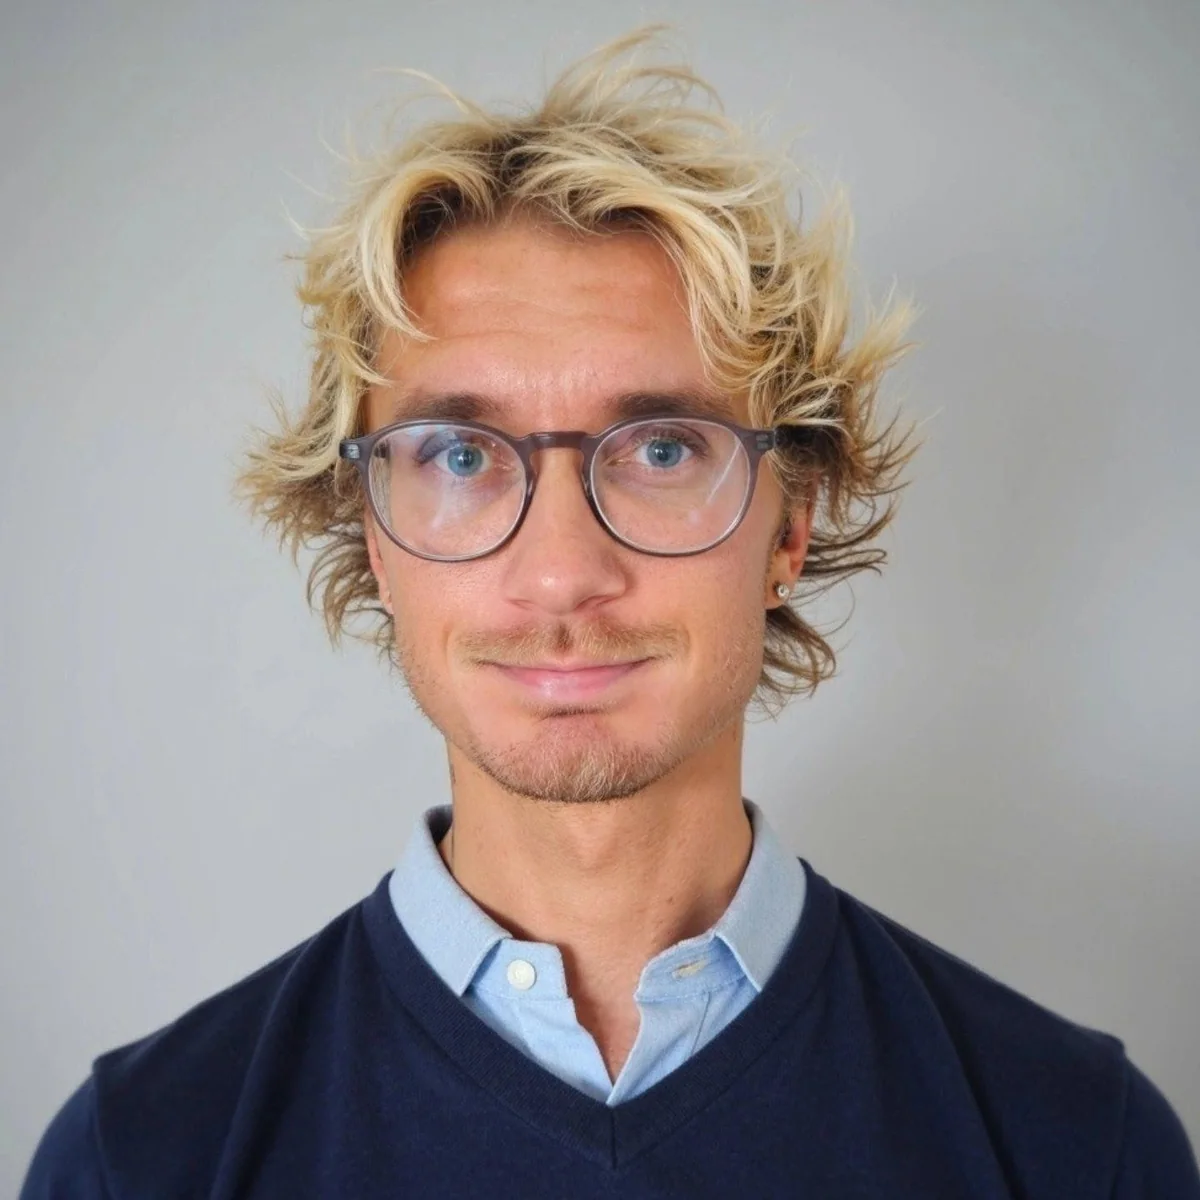
“Far too many systems in use today depend entirely on companies run from the other side of the world. It has gone too far, and we have to deal with it now, before the problems get even bigger. That is why I have worked on this for a long time, with Norway, Scandinavia and the EU first. This is about control. We have to be able to control our own data.”
What Norway can do this winter
The government's working group on Norway's digital room for manoeuvre delivered its advice before the summer. In August the ministry told Altinget that the report was an internal working document, with no summary to share. After this week, the first step is to publish what the group recommended.
Norway can then act on four points, all within its own powers.
Public procurement. State and municipal tenders for email, files and messaging should require data and operations under European law, export of mail, calendars and documents in open standards, and an exit plan the supplier has tested.
Moving. Every ministry, municipality and hospital trust should map what it has with American suppliers and make a plan to move email, files and documents to services under European law. A reserve is not enough when the whole office runs on one supplier from another part of the world.
European law. Services that carry the communication of the state should be operated by companies under European jurisdiction, in data centres in Europe.
Open standards. The government said in April that it would update the regulation on IT standards to require open formats. That change should come into force, so that moving from one supplier to another is a project of weeks.
What we build in Stavanger
Cartaia is the Norwegian alternative: email, files, documents and calendar, built by a Norwegian company in Stavanger. We build it for Norway first, then for Scandinavia and the rest of Europe. The data is in Europe, on servers in Germany with backups in Finland. On 12 and 13 November, Cartaia ran through the outage, sign-in with BankID included.
Cartaia is built to take over the whole office. A municipality, a hospital trust or a business can move its email, files, documents and calendar to Cartaia, and we do the move together with them. The data stays in Europe, under European law, in open formats. The tools exist. Norway can decide this winter to use them.